Free platform scans
Your builder runs free automated checks. Use them. But they can’t tell you which warnings matter for your app, and they don’t fix anything.
Who fixes it You do
For founders who built their app with Lovable, Bolt, Replit, v0 or Cursor
I’m Vikrant, a software engineer. I check your app before real customers arrive, confirm every problem myself, and tell you in plain English what to fix first. If you like, I’ll fix it too.
Findings
4 confirmed · most urgent first
Fix now
Anyone can read your customers’ details
Customer data
Fix today
Orders can be marked paid without paying
Payments
This week
Nobody is told when the app breaks
Monitoring
Noted
Browser security settings missing
Hosting
AI builders are brilliant at getting you to launch. Checking what they built is a different job, and the tools for it assume you can read code.
Your builder runs free automated checks. Use them. But they can’t tell you which warnings matter for your app, and they don’t fix anything.
Who fixes it You do
Long lists of maybes. If you can’t read code, you can’t tell the real problems from the noise.
Who fixes it You do
I confirm what’s real, find what the tools miss, and explain it in plain English. Then, if you want, I fix it.
Who fixes it I can, at a fixed price
In 2025 a security researcher scanned 1,645 public Lovable apps and found 170 of them, about 1 in 10, letting strangers read their users’ data.
Six places where apps built this way most often go wrong. Every Launch Check covers all of them.
Whether a stranger, or one of your own customers, can see data or files that aren’t meant for them.
Whether the pages meant only for you, or only for paying customers, are really locked.
Whether you get paid for every order, nobody is charged twice, and two people can’t book the same slot.
Whether the keys that control your app have ended up somewhere a visitor can find them.
Outdated parts with known security holes, and the protections your hosting should switch on.
Whether you’d know if your app broke, whether your backups restore, and whether your emails reach inboxes.
I use my own tooling, including AI-assisted checks, so nothing gets skipped. Then I confirm every finding myself. Anything I can’t confirm stays out of your report.
No hourly meter. You know the price before I start.
$0
A quick human look at what anyone can see from outside your app.
$249 per app, one time
A full review of your app’s code and live site.
Includes the fixes
$449 per app, one time
The review, and I fix what’s urgent.
Bigger jobs Need more than a day of fixes? I’ll tell you before I start and quote a fixed price for the rest.
Refunds Not happy with your report? Tell me within 7 days and I’ll refund you.
From your first message to your report.
Two minutes
Use the form below. Tell me your app’s address and confirm it’s yours.
Within 48 hours
One to three specific things I noticed, or an honest “nothing obvious from the outside”.
When you’re ready
Pay the fixed price, then invite me to your project on GitHub and Supabase. You can remove me any time.
3 business days
Plus a 30-minute call. With + Fix, I send the fixes for your OK and check them again.
You’re trusting a stranger with your app. Here’s how I handle it.
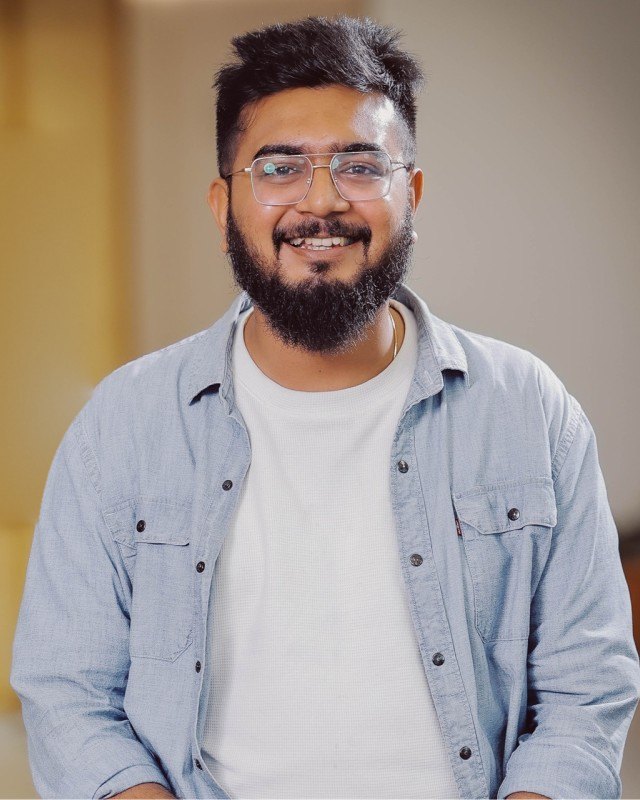
I’m a software engineer based in India. I spent five years at LinkedIn, and these days I build tools that test AI agents, so I know how often AI-written code looks finished when it isn’t, and why I don’t trust it unchecked.
I built my own review tooling so nothing gets skipped. But the judgement is mine, and so is the accountability: my name is on every report.
It’s for apps that are live or launching within weeks, and that take payments or store customers’ data. If yours has no users and no data yet, the free platform scans are enough for now. If you need a certificate, SOC 2 or a formal pentest, this isn’t that. And if your app needs a rebuild rather than fixes, I’ll say so plainly.
Yes, as a tool. I run my own scanners and AI-assisted checks so nothing gets skipped. Then I read the code that matters myself, confirm or throw out every finding, and write every fix. Anything I couldn’t confirm stays out of your report.
No. It’s an honest review of your app as it is on the day I check it, with a clear list of what I checked and what I couldn’t. I don’t sell “secure” badges: nobody can honestly promise an app is 100% safe.
Most builders, including Lovable, Bolt and Replit, can connect your project to GitHub in a couple of clicks, and I’ll walk you through it. If yours can’t, say so in the form and we’ll find a way.
Then your report says so, along with everything I checked. That’s worth knowing before you launch, and it gives you a record of what was checked if a customer or investor ever asks.
No. I review your code and what your live app exposes. Anything that needs accounts, I test with test accounts we set up together.
As changes you approve before anything goes live, or we go through them together on a call. If your builder syncs with GitHub, as Lovable does, it picks them up automatically.
My working day overlaps with US mornings and European working hours, so we can always find a call time that suits you. Everything else happens in writing.
Tell me about your app. I’ll look at what anyone can see from the outside and reply within 48 hours.